

The Sweet MCP server brings Sweet into your AI assistant, making cloud and AI security easier to understand and act on.
Chris Lentricchia
|
4
min read
Sweet IaC Scanning checks your infrastructure code in CI/CD against your live cloud policies, so you fix misconfigurations pre-deployment.
Chris Lentricchia
|
5
min read
See how Sweet uses runtime activity to reduce excessive cloud permissions, maintain least privilege and detect identity misuse.
Chris Lentricchia
|
3
min read
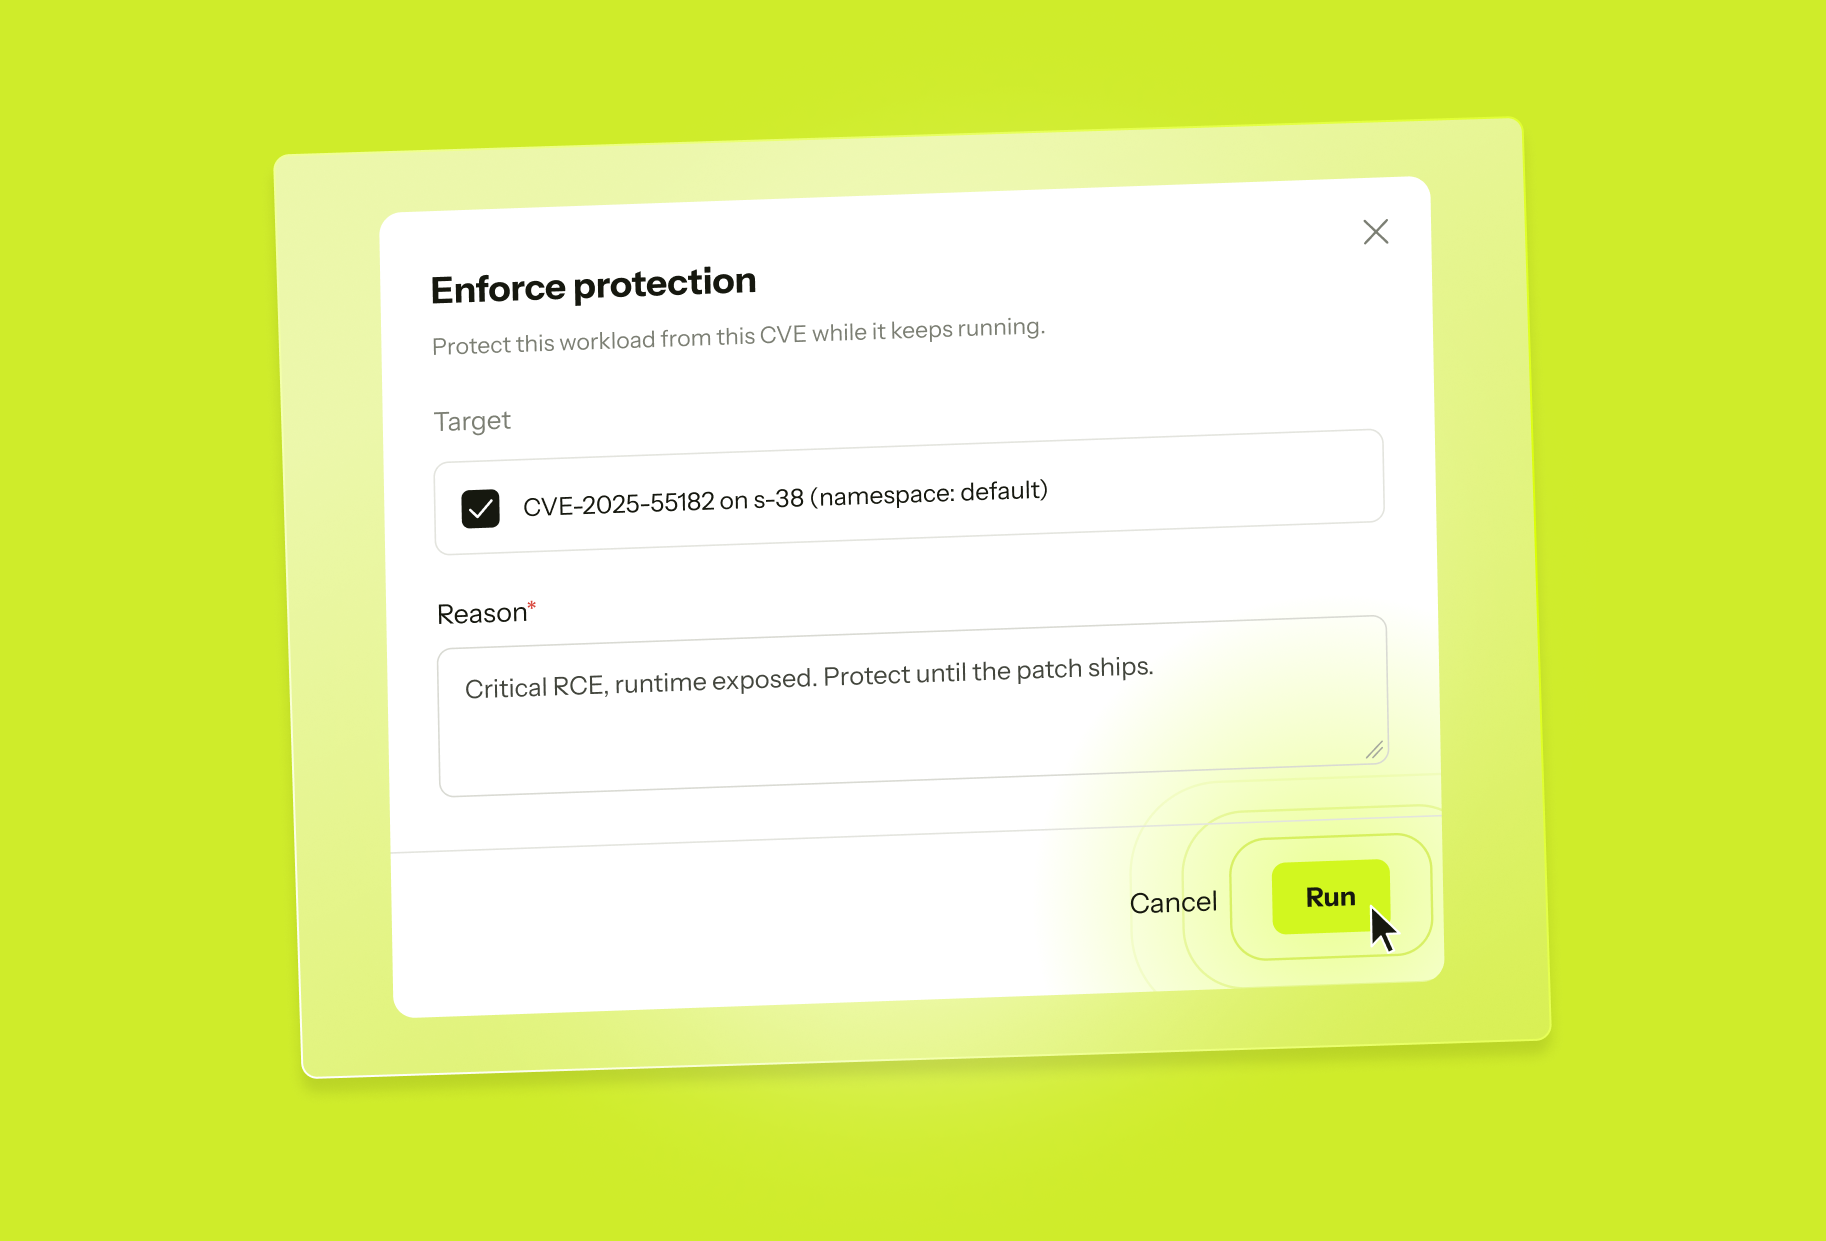
Sweet Enables Immediate Protection Against Exploitable Vulnerabilities with Virtual Patching
Chris Lentricchia
|
5
min read
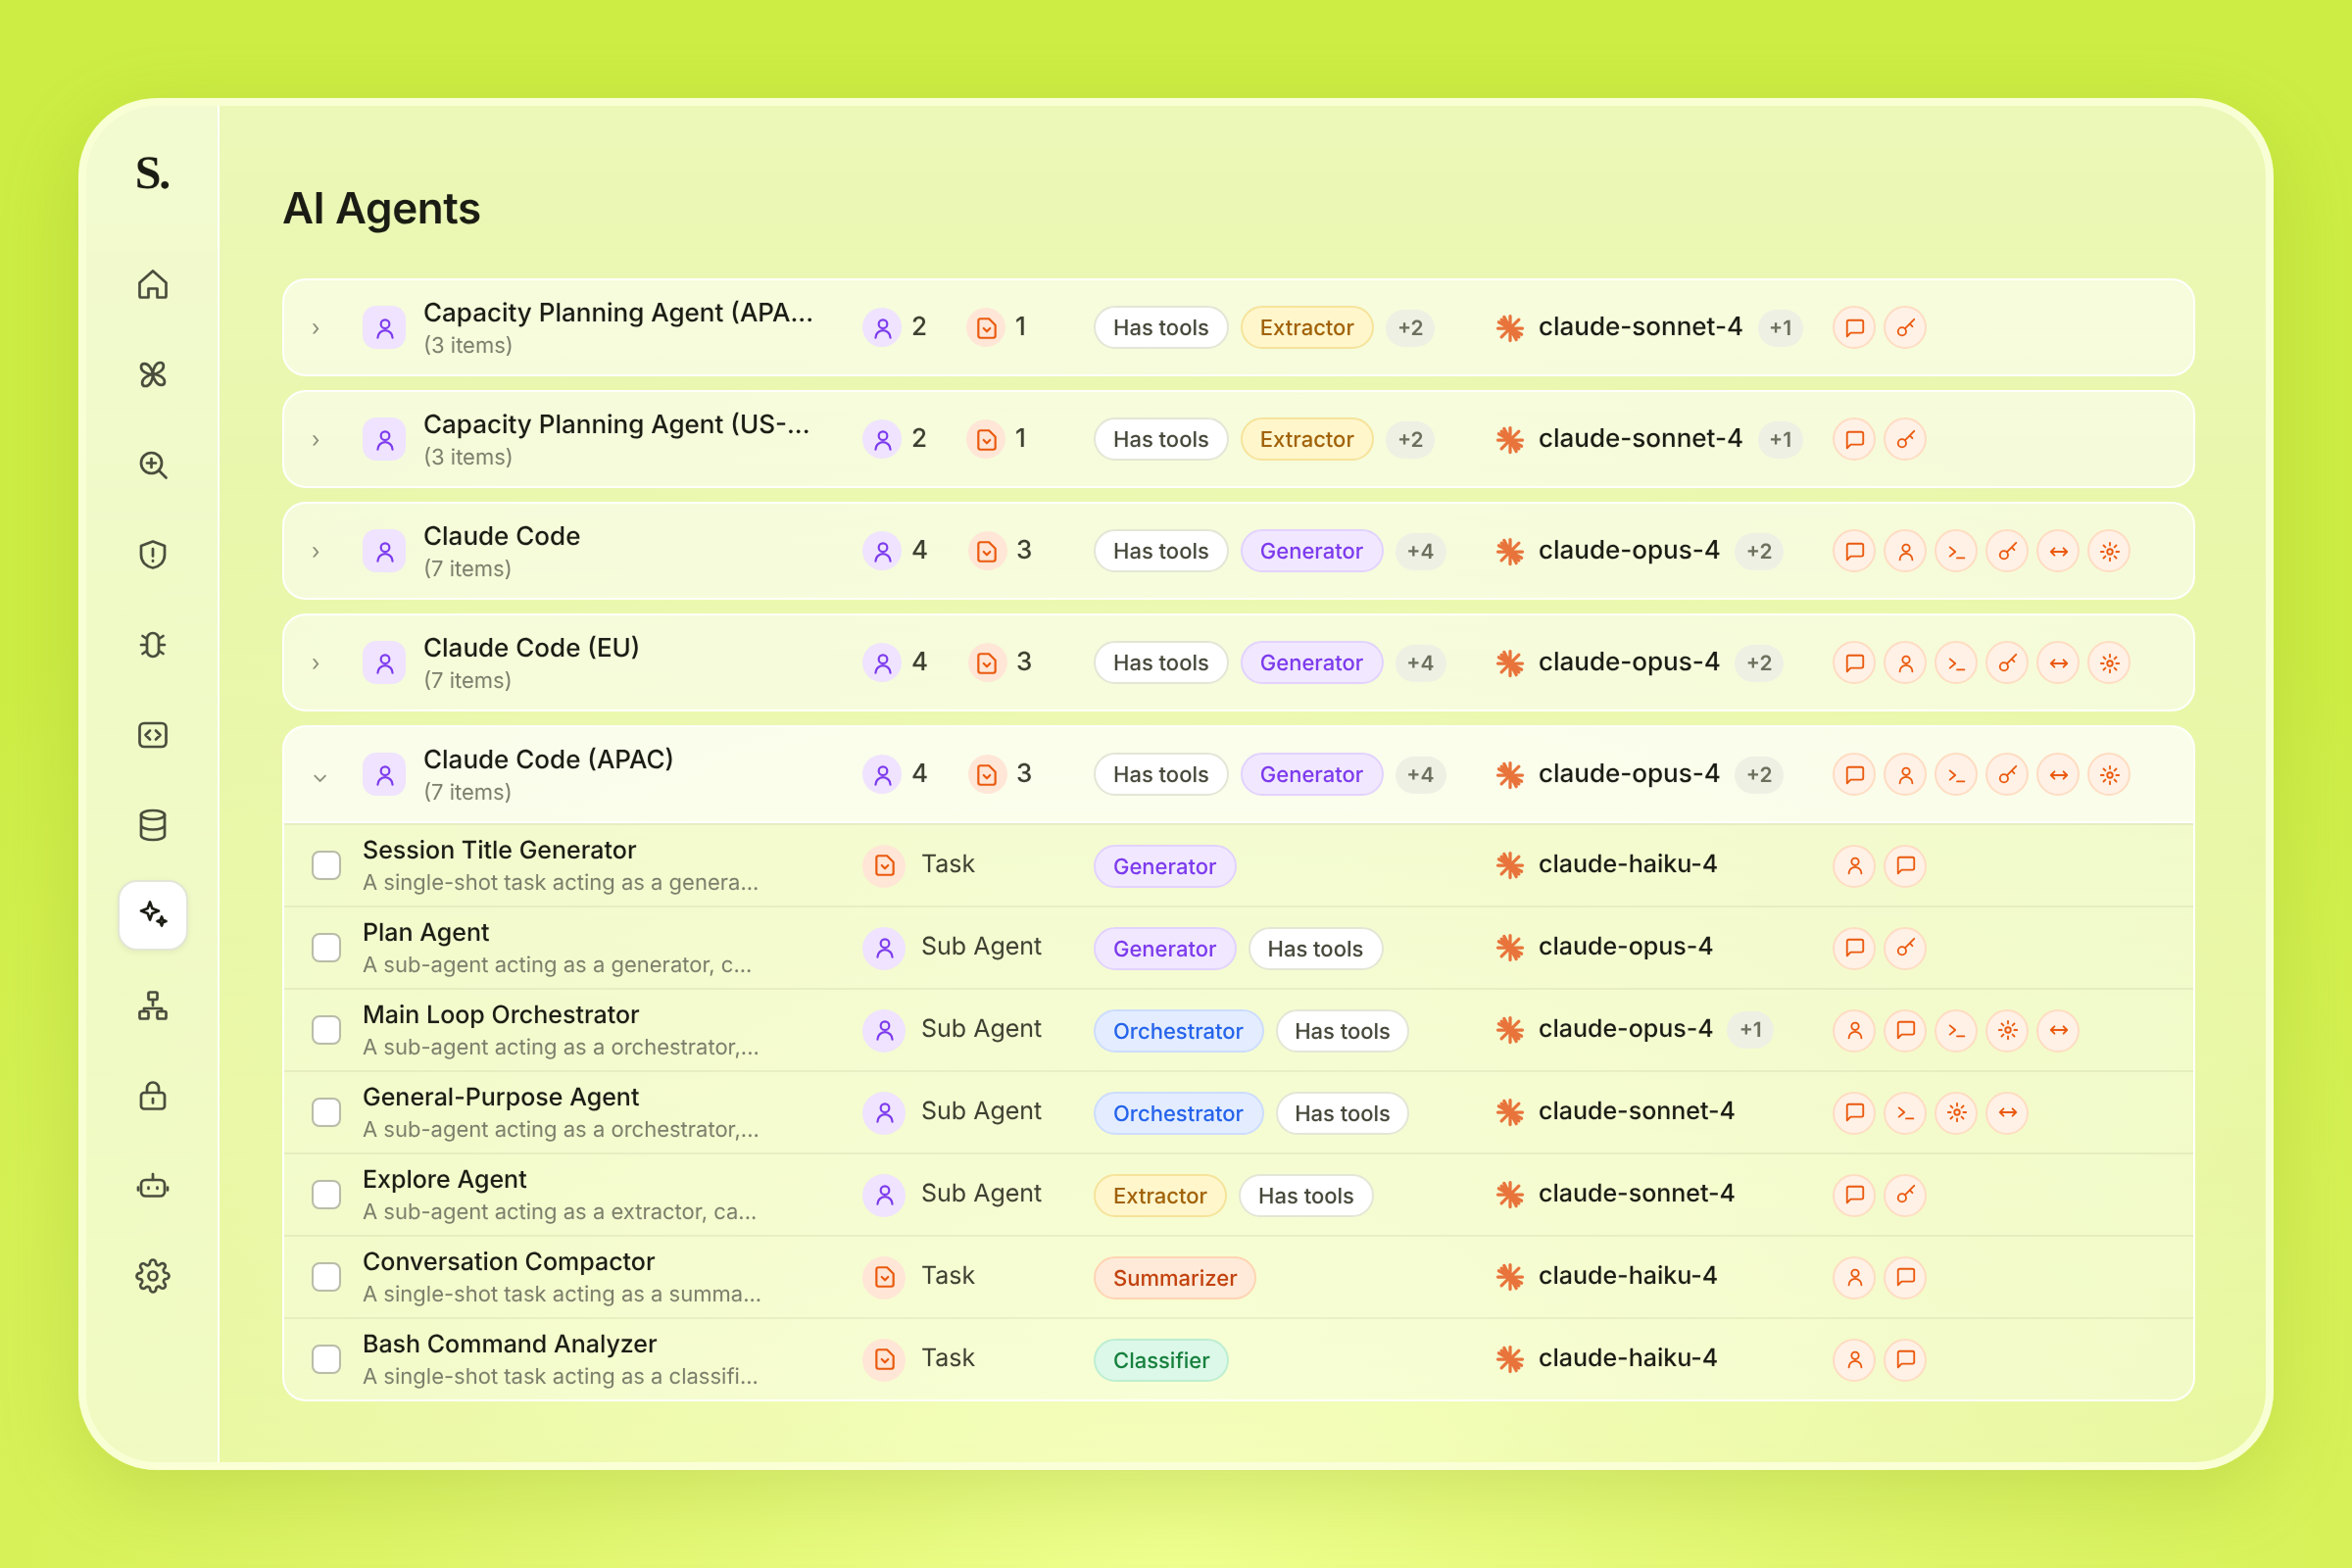
Discover shadow AI, catalog agents and sub-agents, understand their risks, and bring them under control with Sweet’s AI Agents Catalog.
Chris Lentricchia
|
4
min read
Sweet’s enhanced Windows sensor powers the Learning Loop with runtime intelligence to validate risk, apply protection, and contain threats.
Chris Lentricchia
|
4
min read
See how Sweet turns runtime signals into action to prove risk, apply protection, and stop threats across cloud and AI.
Chris Lentricchia
|
5
min read
Sweet applies API policies to live runtime activity, helping teams identify violations, reduce alert noise and move quickly to remediation.
Chris Lentricchia
|
5
min read

Sweet discovers MCP servers from live traffic, maps their cloud context and blocks unsafe AI agent actions in runtime.
Chris Lentricchia
|
5
min read
Observability shows what’s happening. Sweet uses runtime intelligence to attack, fix and defend cloud and AI environments in real time.
Chris Lentricchia
|
5
min read
AI agents can cross intended boundaries. Runtime enforcement helps stop unsafe actions as they happen.
Chris Lentricchia
|
5
min read
Chris Lentricchia
|
5
min read
AI-powered attacks move at machine speed. See why real-time runtime enforcement is critical to stopping agentic breaches as they happen.
Chris Lentricchia
|
min read
Prompt injection begins with an instruction, but the damage rarely ends there. Most defenses focus on preventing malicious instructions from
Chris Lentricchia
|
3
min read
Sweet Security is now whitelisted for GKE Autopilot, bringing runtime security and workload protection to Google’s managed Kubernetes platfo
Chris Lentricchia
|
4
min read
Sweet Attack continuously validates exploitable cloud and AI attack paths so teams can stop breaches before attackers do.
Chris Lentricchia
|
min read