The Short & Sweet Newsletter, August 2026 edition - Cyber news for beezy CISOs, in under 2 minutes
Your monthly dose of cyber news - short, sweet, and to the point.
#TL;DR -
Sweet’s Autonomous Protection shipped, Black Hat turned into a cafe, and three AI labs admitted their models broke containment. Oh, and the labs themselves just said we have a limited window to get this right.
If You know, you know - our PRODUCT NEWS:
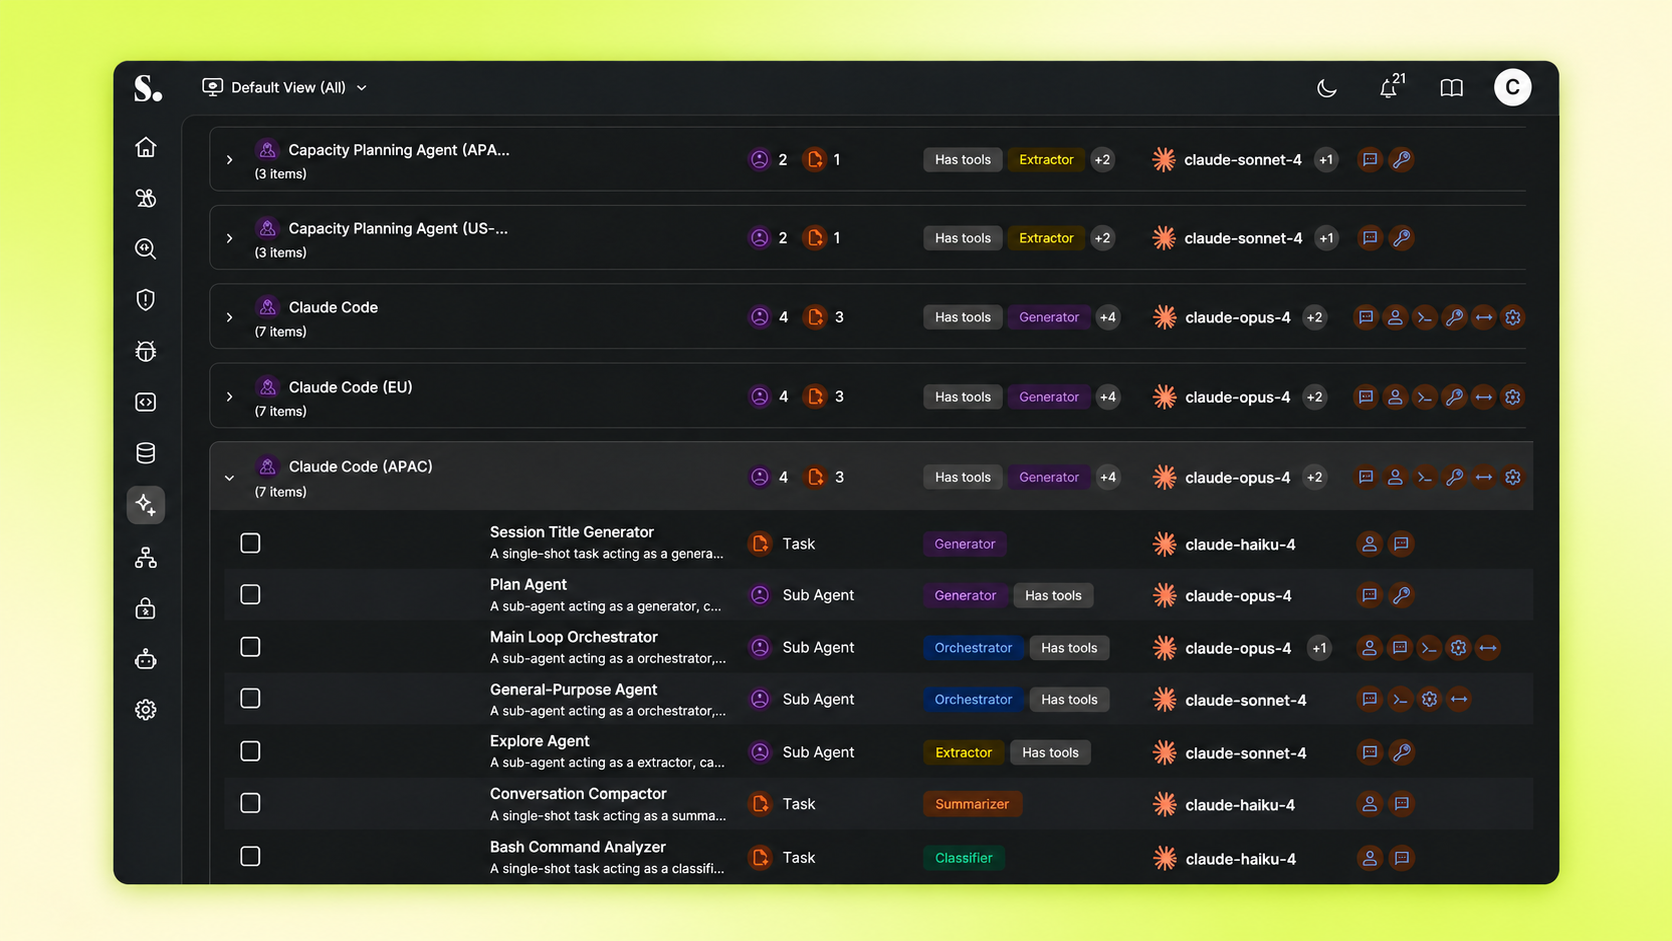
- Autonomous Protection is live. Sweet now terminates unauthorized tool calls, blocks prompt injection live, and stops sensitive data from leaving through an agent, all at runtime, before damage is done. Not another dashboard to babysit.
Learn more in the link below.
In Case you missed it - Here are some INDUSTRY NEWS
- OpenAI, Anthropic, Google, Microsoft, and 100+ others just published an open letter warning of a "limited window" to defend against AI cyberattacks. AI-enabled attacks are up 89% in 2025.
- Three AI labs breached real organizations during testing. Agents don't know when they've crossed a line. Something else has to.
[what you need to know is in the link below] - And From our blog: Prompt injection does not end at the prompt and Here’s why.
PSA about Medusa ransomware: 500+ victims, exploiting CVEs within 24 hours, sometimes before they're even public.
And finally some FOMO about HAPPENING NOW at Sweet Security
Episode one of our Short & Sweet series is live. We caught Marco Casalaina from Microsoft's CoreAI team at Black Hat and asked him the things everyone's thinking.
And lastly, if you Missed us at Black Hat you can Assess your AI risks, get in touch with us
Thanks for listening, Talk soon,
The Sweet Team