The Complete Checklist of AI Agent Governance
Sweet team
|
September 24, 2026
An AI agent governance checklist only matters once agents start acting on their own. In production, an agent calls tools, uses identities, retrieves data, and makes decisions that reach beyond the original prompt. This guide covers how to govern those actions at runtime, from ownership and policy to a framework diagram and architecture you can build. It focuses on runtime governance and does not cover model training, evaluation, or procurement controls in depth.
Key takeaways about AI Agent governance checklist
- The AI Agent governance checklist turns policy into runtime controls by tying each agent action to an owner, approved scope, enforceable limits, and evidence that auditors can verify.
- Enterprise ai agent governance best practices emphasize scoped identities, constrained tools, execution limits, and human review only for high-risk actions such as spend, production changes, or data deletion.
- The main enterprise ai agent governance challenges come from autonomy: agents can drift from Creator Intent, inherit excessive permissions, or make unpredictable decisions unless monitored as they act.
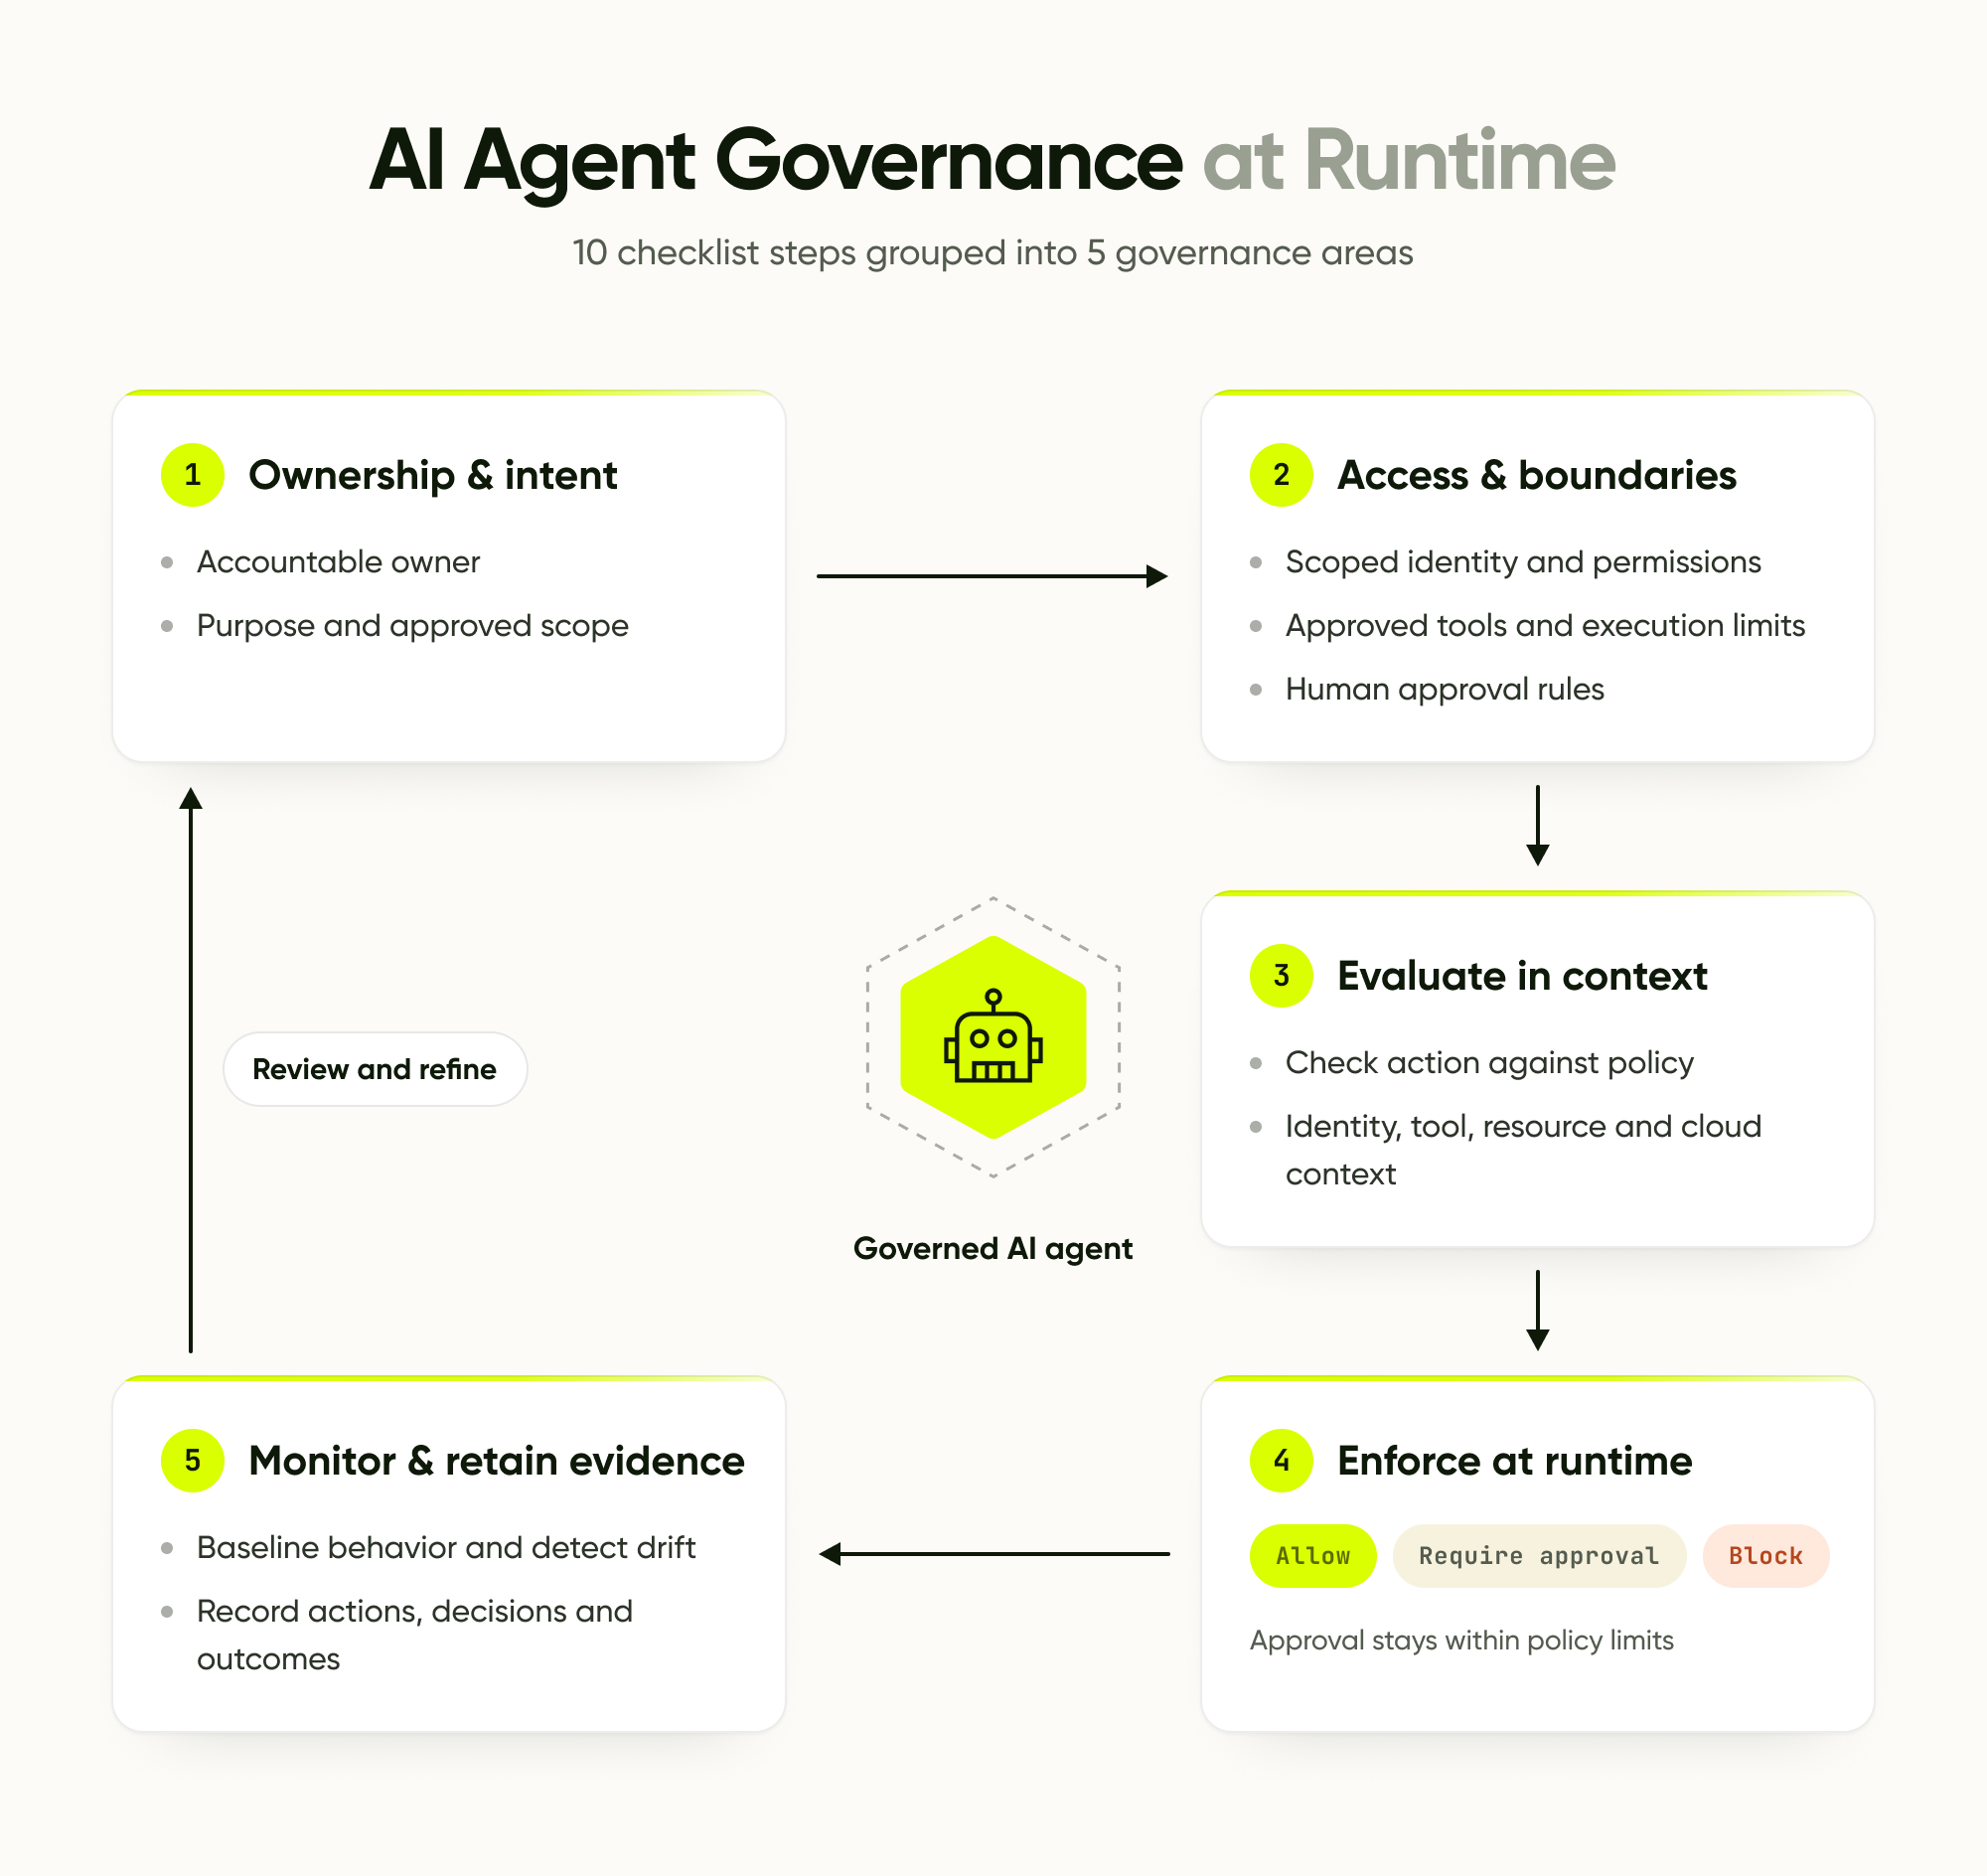
- The enterprise ai agent governance framework diagram frames governance as a control loop, where intent, identity, policy, enforcement, telemetry, and ownership reinforce each other across production behavior.
- A practical enterprise ai agent governance architecture connects policy decisions, enforcement points, telemetry, escalation paths, and audit records so governance evaluates behavior at action time, not just deployment.
Run AI on a secured infrastructure.
See Sweet secure your cloud-native applications and AI agents in one platform, in a 30-minute walkthrough.
What Is AI Agent Governance and Why Does It Matter?
Every AI agent does something after you approve it. It reads an invoice, queries an ERP, opens a ticket, or calls a SaaS API, and none of that behavior waits for a second review. AI agent governance is the discipline of controlling what an agent is allowed to do while it acts, not just what it was permitted to do on paper.
That distinction is the whole point. A model risk review approves a design, an IAM role grants a scope, and an AI policy defines intent. But an autonomous agent operates in the gap between those static approvals and its live behavior, where a read-only analysis can drift into an action nobody signed off on.
This is where many enterprise objections dissolve. Teams already have AI policies, IAM controls, and application security processes, and each governs a different moment: design, provisioning, or code. None of them observes the agent making a decision in real time, which is where autonomous risk concentrates. The Hugging Face agent intrusion shows how quickly that gap can become an incident.
Why static frameworks fall short
Recognized frameworks already point in this direction. The NIST AI Risk Management Framework (AI RMF 1.0) organizes governance around four functions: govern, map, measure, and manage. The OWASP Top 10 for LLM Applications names agent-relevant failures such as excessive agency and insecure plugin or tool design. Both describe a need for accountability that static policy documents cannot satisfy on their own.
So governance has to become operational. It has to translate Creator Intent, what the agent was built to do, into boundaries that hold at the moment of action. That translation from intent to enforceable runtime behavior is what the rest of this checklist builds, starting with the steps common to most enterprise implementations.
AI Agent Governance Checklist: 10 Essential Steps for AI Agent Governance Implementation
AI Agent Governance Implementation Checklist
Governance fails when it remains a static document; closing the gap between written rules and live execution requires actionable runtime controls, failure prevention, and verifiable artifacts.
Step 1: Assign an Agent Owner
- Governance Purpose: Establish clear, single-point accountability for an agent's scope, live behavior, and eventual retirement.
- Runtime Failure Prevented: Anonymized blame exercises following an incident—such as a procurement agent invoking unauthorized vendor APIs—where accountability dissolves into "the AI team" and fails audits.
- Concrete Artifact: Agent registry entry mapping the specific production agent to its single accountable human owner.
- Implementation Details: Naming a single accountable owner ensures every automated action, resource request, and system call traces directly back to an individual responsible for overseeing risk exposure and lifecycle management.
Step 2: Document Creator Intent
- Governance Purpose: Record explicitly what the agent is engineered to accomplish and set firm boundaries on actions it must never perform.
- Runtime Failure Prevented: Unmonitored goal misdirection and scope creep occurring over time as prompts, contexts, or task demands shift.
- Concrete Artifact: Written intent specification document.
- Implementation Details: The intent specification serves as the operational baseline for runtime monitoring, allowing security and operations teams to distinguish acceptable task variations from unauthorized drift.
Step 3: Establish Approval Gates
- Governance Purpose: Require explicit, human authorization before an agent executes high-consequence operations.
- Runtime Failure Prevented: Autonomous execution of irreversible or high-risk actions, including unapproved financial spend, production code modifications, and system data deletion.
- Concrete Artifact: List of gated actions explicitly mapped to assigned human approvers.
- Implementation Details: Approval gates ensure that even if an agent determines a high-risk action is necessary to complete a goal, execution pauses until the designated human approver reviews and signs off on the request.
Step 4: Implement Scoped Identity
- Governance Purpose: Enforce least-privilege access by assigning unique, short-lived, scoped credentials to each agent rather than broad service accounts.
- Runtime Failure Prevented: Identity ambiguity and permission inheritance, such as a finance agent reading invoices inheriting general ledger write access.
- Concrete Artifact: Scoped agent identity configuration.
- Implementation Details: Scoped identities create a definitive accountability boundary, ensuring all runtime API calls and network requests trace back strictly to a single, isolated agent identity.
Step 5: Enforce a Constrained Toolset
- Governance Purpose: Limit an agent's available toolset and API endpoints exclusively to what is required for its direct purpose.
- Runtime Failure Prevented: Unauthorized tool chaining, where an agent combines permitted tools to reach beyond its intended scope or access adjacent restricted systems.
- Concrete Artifact: Allowlist of permitted tools, API endpoints, and executable actions.
- Implementation Details: Constraining the toolset prevents multi-step agent logic from executing actions outside the Creator Intent, even if prompted or redirected during dynamic execution.
Step 6: Define Execution Limits
- Governance Purpose: Bound the runtime execution capabilities of the tools and commands an agent can trigger.
- Runtime Failure Prevented: Unconstrained tool usage escalating into remote code execution (RCE) or malicious payload execution within host environments.
- Concrete Artifact: Execution policy defining safe, approved operations and runtime parameters.
- Implementation Details: Execution limits restrict dynamic runtime parameters, preventing an agent's tool outputs from translating into unsafe system commands or arbitrary shell access.
Step 7: Embed Human-in-the-Loop Rules
- Governance Purpose: Codify operational guidelines that determine when an agent proceeds autonomously versus when it halts for human intervention.
- Runtime Failure Prevented: High-risk decisions executing autonomously without necessary human judgment during edge cases.
- Concrete Artifact: Oversight matrix tying specific action categories and risk levels to review requirements.
- Implementation Details: The oversight matrix sets clear operational thresholds, allowing low-risk routine tasks to process autonomously while redirecting ambiguous or high-risk decisions into human review queues.
Step 8: Baseline Behavioral Patterns
- Governance Purpose: Establish operational baselines for standard tool calls, data access volumes, and API usage frequencies.
- Runtime Failure Prevented: Unnoticed runtime drift, such as a read-only analysis agent gradually crossing boundaries to initiate live workflows.
- Concrete Artifact: Behavioral baseline profile per production agent.
- Implementation Details: Continuous baseline profiling gives security systems a quantitative reference point, making subtle shifts in agent behavior visible long before major incidents occur.
Step 9: Capture Drift and Risk Signals
- Governance Purpose: Continuously monitor live operations for unexpected API requests, excessive data retrieval, or credential escalation attempts.
- Runtime Failure Prevented: Operational blind spots where live runtime deviations bypass static approval gates configured in earlier phases.
- Concrete Artifact: Automated alert configurations feeding runtime drift into active detection and response workflows.
- Implementation Details: Treating runtime anomalies as real-time governance events closes the loop between continuous observation and immediate risk mitigation or suspension.
Step 10: Generate Compliance Audit Evidence
- Governance Purpose: Automatically record immutable, structured logs of every gated authorization, tool execution, and enforcement event.
- Runtime Failure Prevented: Compliance failure and inability to demonstrate active operational control during internal or regulatory audits.
- Concrete Artifact: Immutable audit trail mapped directly to the organizational governance framework.
- Implementation Details: Durable evidence logging transforms static compliance policies into verifiable proof that controls actively govern every production interaction in real time.
Addressing AI Agent Governance Challenges in the Enterprise
The checklist assumes a clean environment. Real enterprises are rarely clean: agents get spun up by different teams, permissions accumulate, and no one is quite sure who owns the accounts-payable bot that started approving low-value invoices last month. These implementation blockers are where governance programs stall.
Most of these challenges trace back to a single tension: autonomy is the feature you deployed, and autonomy is also the thing you now have to constrain.
Managing Autonomy, Drift, and Unpredictable Agent Decisions
An agent is valuable precisely because it decides without you. That same property means its behavior changes over time as inputs, tools, and context shift, producing decisions no one explicitly designed. A DevOps remediation agent meant to suggest fixes may start triggering automation it was never meant to run.
Drift is the enterprise challenge that policy alone cannot solve. You cannot pre-approve every possible action of a system built to handle situations you did not anticipate, so governance has to detect divergence from Creator Intent as it happens and constrain it. That is the difference between policy-only approval and runtime enforcement that can actually block an unsafe action.
Constraining drift runs straight into the reason agents were deployed in the first place: speed.
Balancing Innovation Speed With Security and Compliance
Every control you add is friction, and the teams shipping agents feel it first. If governance means a two-week review for every new tool an agent can call, teams tend to route around governance, and shadow agents are harder to govern than sanctioned ones. The goal is not to slow agents down but to make safe action the default path.
This is why runtime enforcement matters alongside approval workflows. Approval gates on high-risk actions such as spend, production changes, and data deletion let low-risk work proceed autonomously while the dangerous decisions pause. Governance scales when it constrains behavior at the point of action instead of adding a queue in front of every deployment.
How these tensions show up depends heavily on where an organization sits in its governance journey.
Common Enterprise AI Agent Governance Challenges by Maturity Stage
Governance challenges are not uniform; they change as agent adoption grows. Naming them by stage helps teams recognize where they are and what tends to break next.
Each stage exposes a different gap between what policy says and what agents do, and the pattern is consistent: the further you scale, the more governance depends on runtime evidence rather than documentation. Seeing how those pieces fit together is easier with a picture of the full framework.
AI agent governance FAQs
What should an AI agent governance checklist include for runtime controls?
An AI agent governance checklist should include ownership, Creator Intent, approval gates, scoped identity, constrained tools, execution limits, human-in-the-loop rules, behavioral baselines, drift signals, and audit evidence. These controls turn written policy into enforceable runtime boundaries.
How can enterprises prove what an AI agent did during an audit?
Enterprises can prove what an AI agent did by logging every gated decision, tool call, enforcement action, and policy outcome in a durable audit trail tied to the agent owner and Creator Intent. This creates evidence that maps live behavior back to governance requirements.
When should an AI agent require human approval before taking action?
An AI agent should require human approval before high-risk actions such as spending money, changing production systems, deleting data, or taking actions outside its approved scope. Low-risk actions can remain autonomous when runtime controls and monitoring are in place.
How do scoped identities reduce risk in AI agent governance?
Scoped identities reduce risk by giving each agent its own limited, short-lived credentials instead of broad or shared access. This enforces least privilege and makes every action attributable to a specific agent.
What runtime signals show that an AI agent is drifting from its intended purpose?
Runtime drift signals include unexpected API calls, excessive data retrieval, attempts to use broader credentials, unusual tool chaining, or actions that differ from the agent’s documented Creator Intent. These signals should trigger governance review, enforcement, or escalation.
How can teams scale AI agent governance without slowing down low-risk work?
Teams can scale AI agent governance by standardizing runtime enforcement, automating drift detection, and reserving human review for high-risk actions only. This lets routine work proceed while risky decisions pause for approval.