See how Sweet uses runtime activity to reduce excessive cloud permissions, maintain least privilege and detect identity misuse.
Chris Lentricchia
|
3
min read
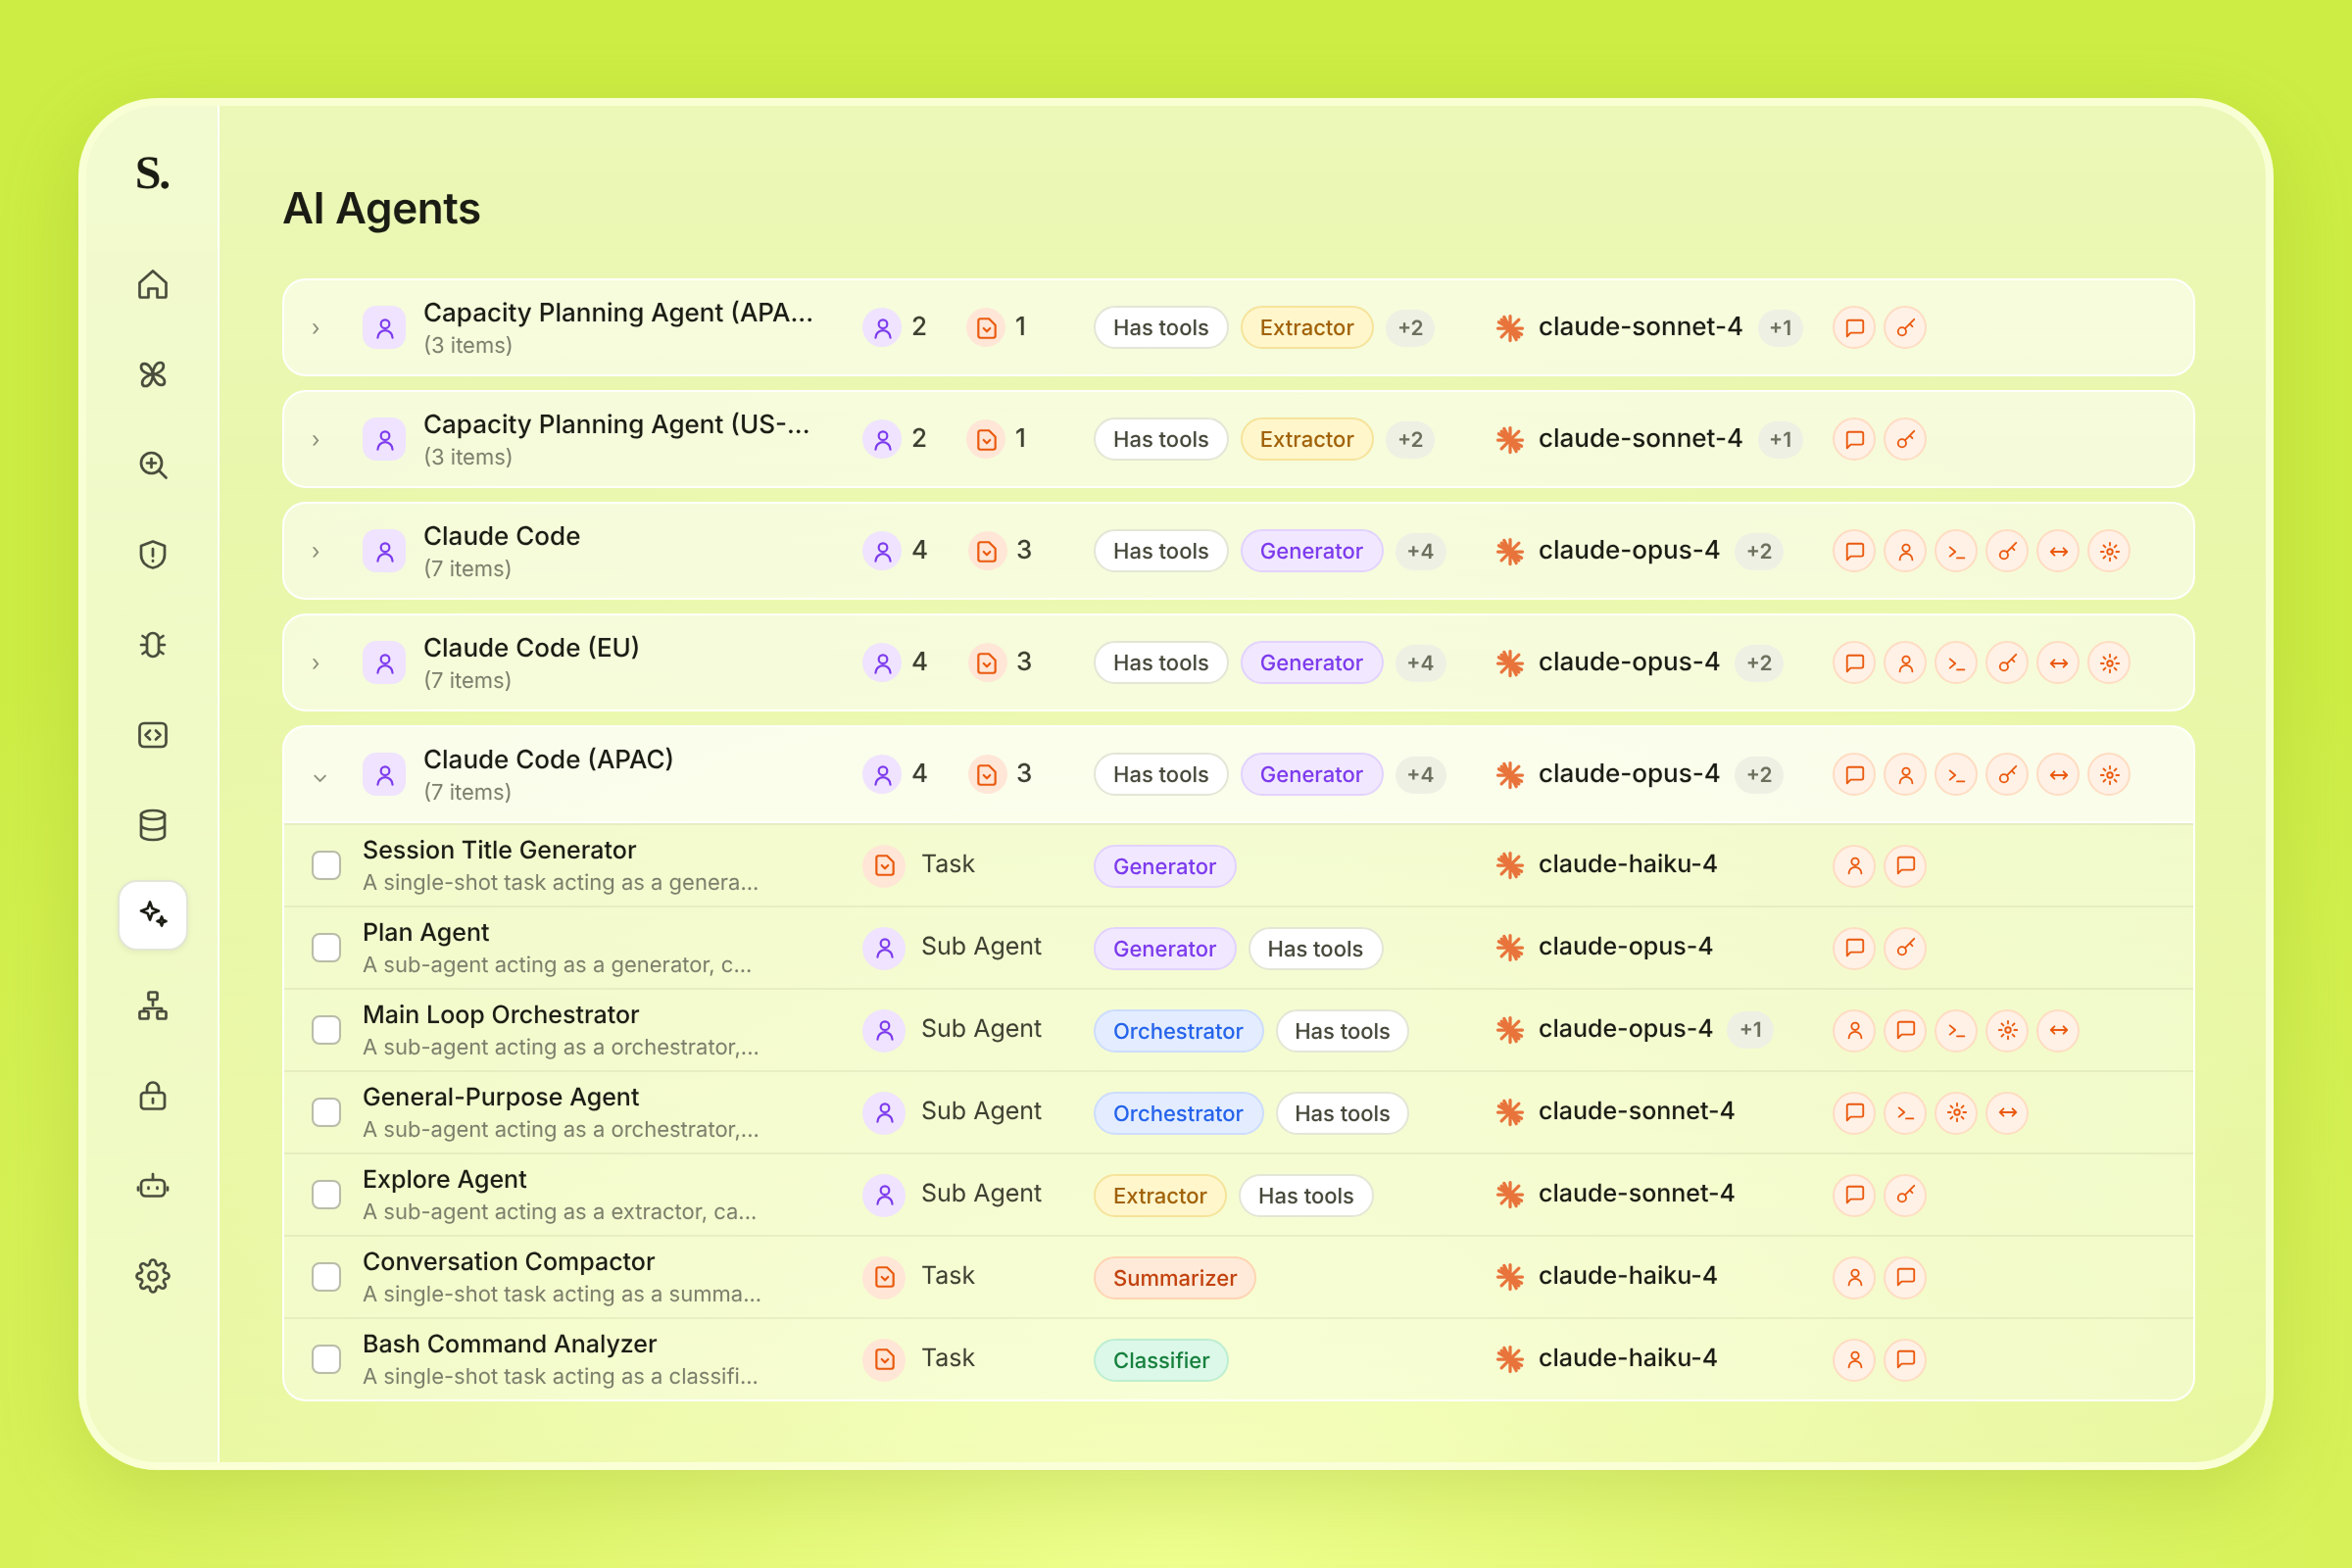
Discover shadow AI, catalog agents and sub-agents, understand their risks, and bring them under control with Sweet’s AI Agents Catalog.
Chris Lentricchia
|
4
min read
Sweet’s enhanced Windows sensor powers the Learning Loop with runtime intelligence to validate risk, apply protection, and contain threats.
Chris Lentricchia
|
4
min read
See how Sweet turns runtime signals into action to prove risk, apply protection, and stop threats across cloud and AI.
Chris Lentricchia
|
5
min read
Observability shows what’s happening. Sweet uses runtime intelligence to attack, fix and defend cloud and AI environments in real time.
Chris Lentricchia
|
5
min read
Chris Lentricchia
|
5
min read
Sweet Security is now whitelisted for GKE Autopilot, bringing runtime security and workload protection to Google’s managed Kubernetes platfo
Chris Lentricchia
|
4
min read
Sweet Attack continuously validates exploitable cloud and AI attack paths so teams can stop breaches before attackers do.
Chris Lentricchia
|
min read
Custom policies in Sweet align security rules to real cloud environments, cutting noise and surfacing only meaningful risks
Sweet team
|
3
min read

Sweet team
|
2
min read

One of Sweet's most powerful features is tracking manual actions and identifying the human identity behind suspicious activity in cloud.
Sarah Elkaim
|
1
min read

Sweet team
|
min read

Sarah Elkaim
|
min read

You Moved Windows Workloads to the Cloud. What’s Next?Sure, your cloud provider secures the infrastructure, but what about the workloads...
Sarah Elkaim
|
min read

Sweet is thrilled to announce a new feature: AI Response Playbooks. This groundbreaking capability is now available on the Sweet Security...
Or Harel
|
3
min read

In recent months, Sweet has expanded its features within the realm of Cloud Vulnerability Management to include the following...
Or Harel
|
4
min read