
CTO
Sweet’s Virtual Patching blocks exploits like Node2Shell at runtime using eBPF, with no code changes, no redeploys, and no downtime.
Tomer Filiba
|
3
min read
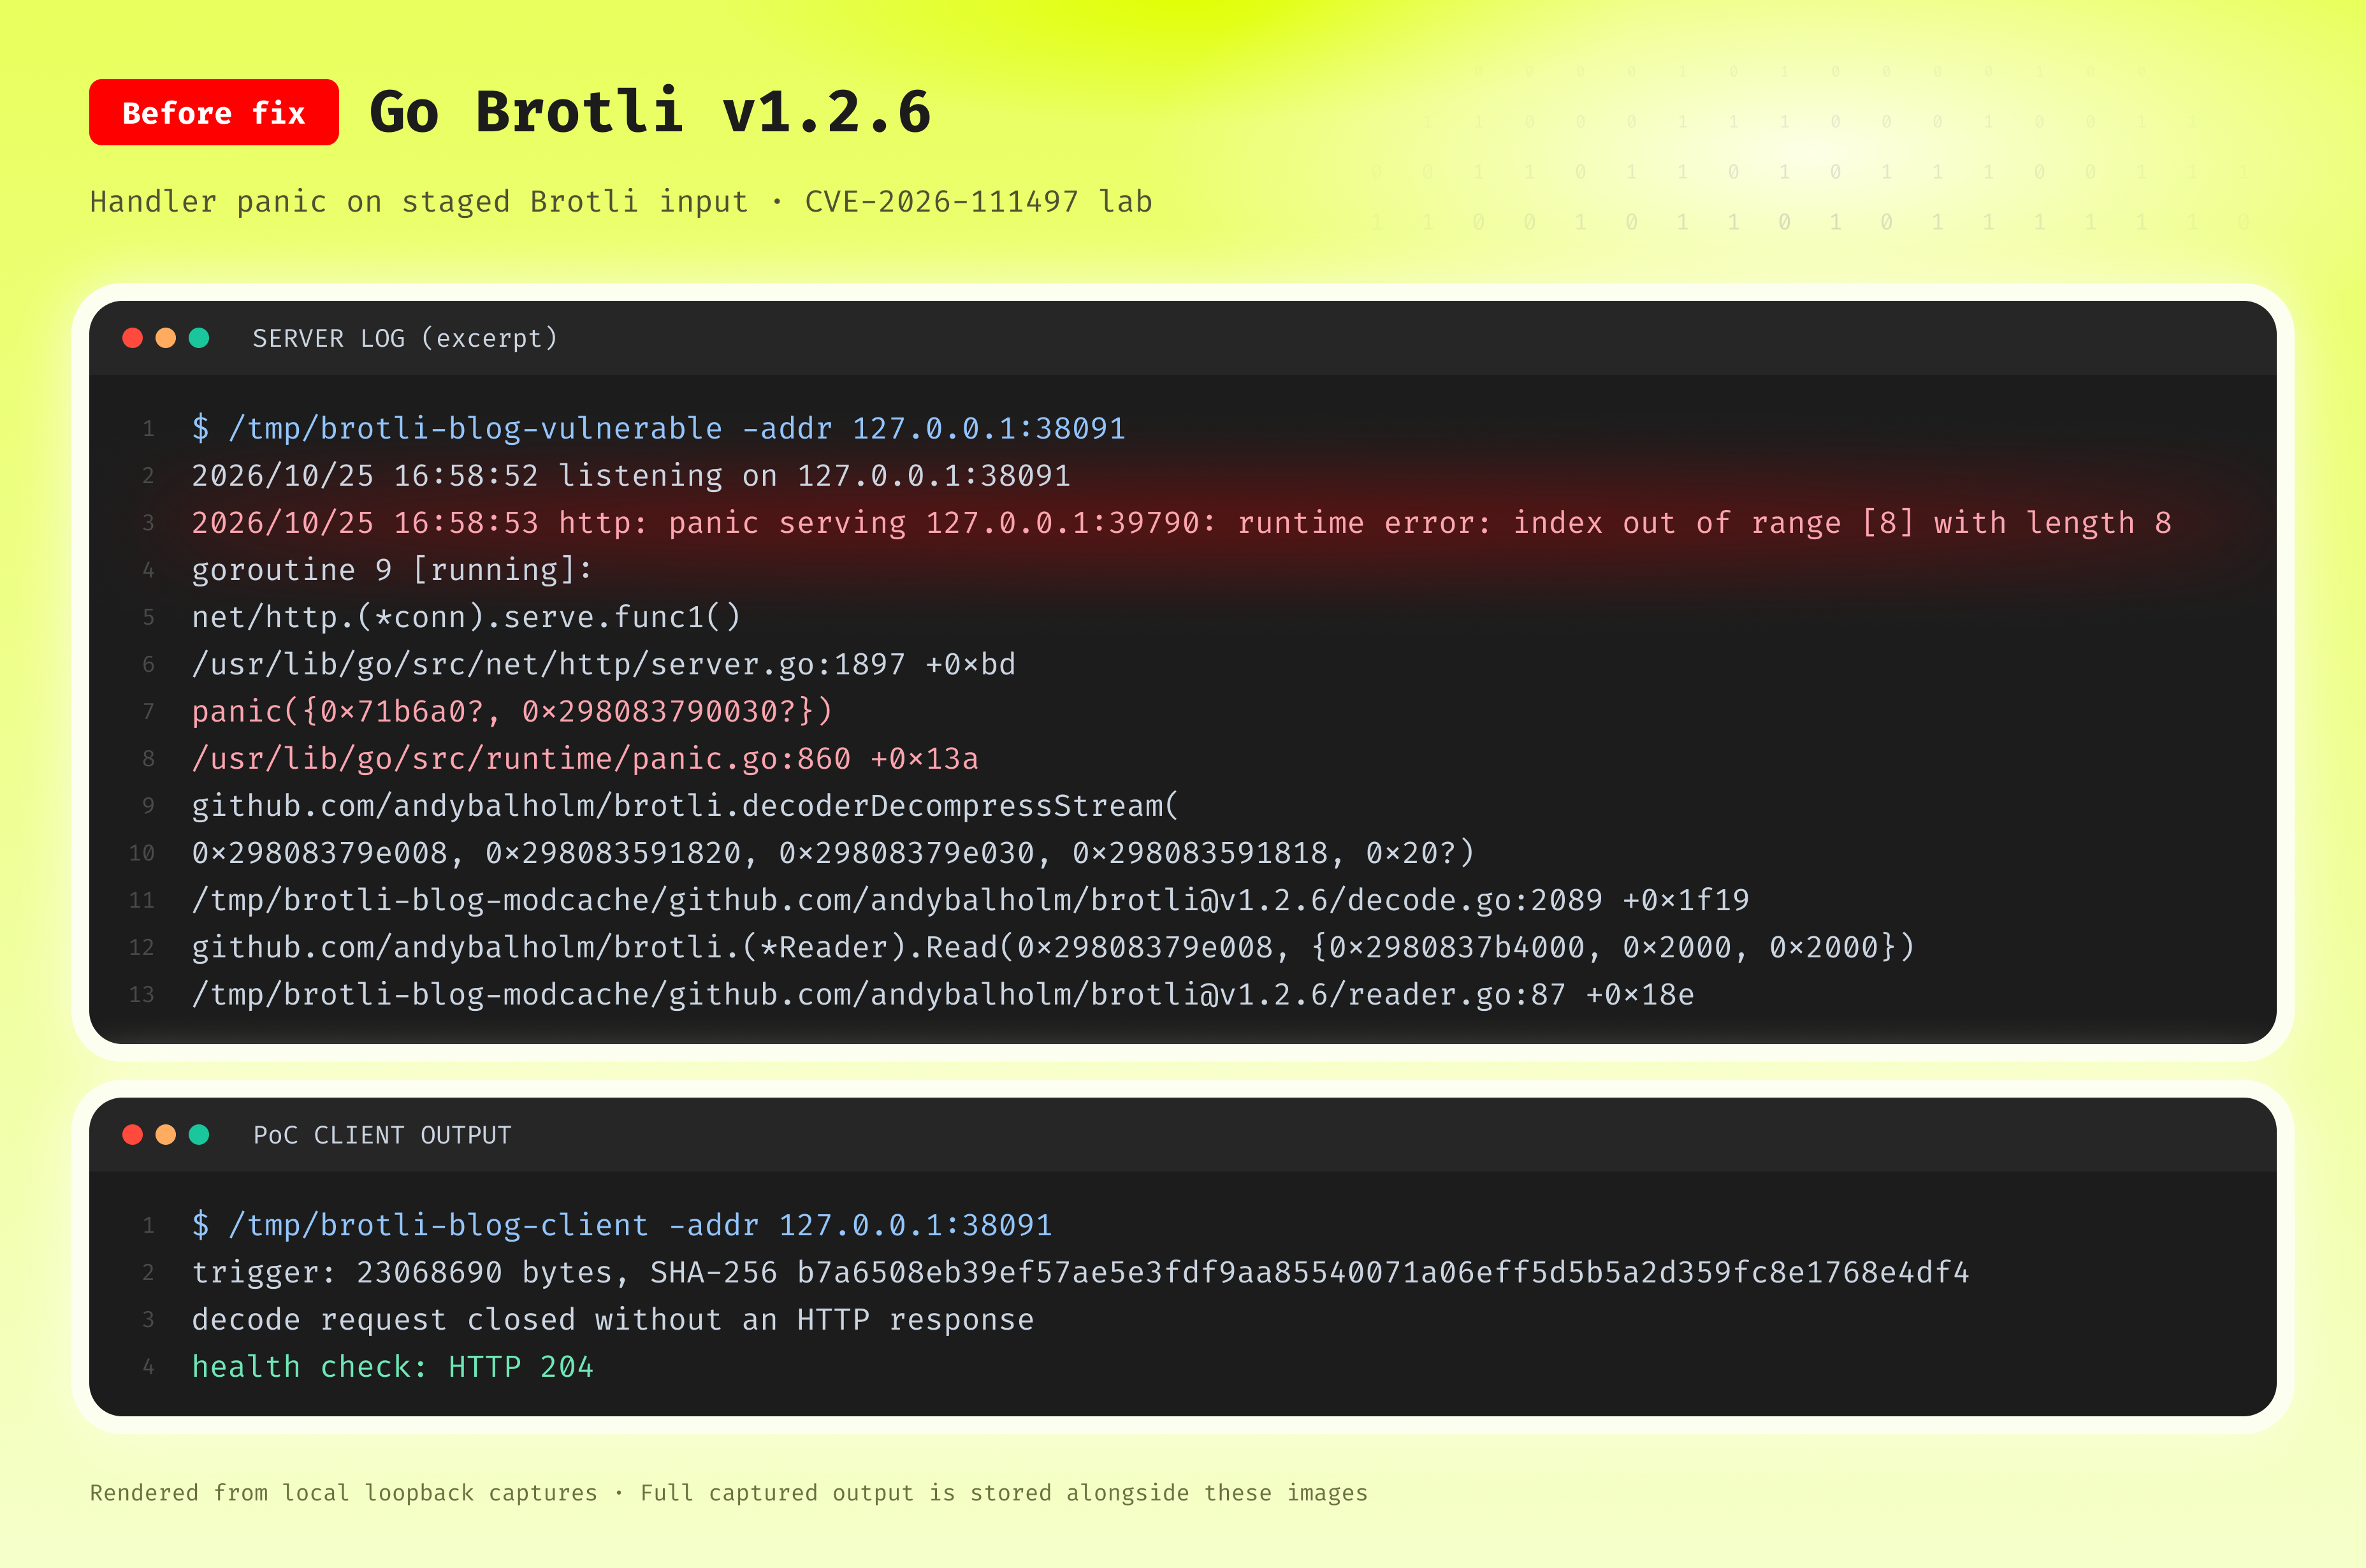
A Go Brotli vulnerability puts applications at risk. Learn which projects are affected and how to investigate exposure and protect productio
Tomer Filiba
|
3
min read
PHP2Shell exposes PHP apps to remote code execution. See which versions are affected and how to patch, detect, and respond to exploitation.
Tomer Filiba
|
5
min read

Autonomous AI changes the rules of cybersecurity. It's time our defenses become autonomous, too.
Tomer Filiba
|
5
min read
The @mastra attack shows why blocking malicious execution and minimizing entitlements are both critical
Tomer Filiba
|
6
min read
A recent compromise of the widely-used axios HTTP client library: npm supply chains can be leveraged to drop cross-platform RATs
Tomer Filiba
|
min read

A standard Kubernetes permission has been identified as a direct path to a cluster-wide RCE.
Tomer Filiba
|
3
min read

The npm ecosystem is once again at the center of a major supply-chain security incident.
Tomer Filiba
|
2
min read
Sweet Security extended its runtime coverage to Windows environments.
Tomer Filiba
|
4
min read
A massive supply-chain attack is affecting npm packages.
Tomer Filiba
|
3
min read
The npm ecosystem has suffered an unprecedented supply-chain attack.
Tomer Filiba
|
2
min read

A critical vulnerability in Python's tarfile module (versions ≥ 3.12) allows attackers to modify metadata or permissions on files.
Tomer Filiba
|
2
min read

Two researchers have recently discovered an authorization-bypass bug in the popular NextJS framework by Vercel. Tracked as CVE-2025-29927
Tomer Filiba
|
2
min read

A new set of high-severity vulnerabilities, collectively dubbed IngressNightmare, has been discovered by Wiz. Sweet keeps you secure.
Tomer Filiba
|
1
min read

On Friday, a supply chain attack compromised the widely used GitHub Action tj-actions/changed-files, exposing secrets from numerous repos.
Tomer Filiba
|
2
min read

The recent XZ (liblzma) supply-chain attack is a marvel of social engineering and a great example of evading detection under the many-eyes..
Tomer Filiba
|
2
min read

Bleeping Computer has recently reported on a new vulnerability within Ghostscipt, a widely used library for handling PostScript and PDF file
Tomer Filiba
|
min read

Yesterday, a new set of vulnerabilities (CVE-2024-47076, CVE-2024-47175/6/7) was discovered on Linux’s Common UNIX Printing System...
Tomer Filiba
|
3
min read

We’re excited to announce that Sweet Security has officially released CandyStore – an extremely fast open source key-value store
Tomer Filiba
|
2
min read